- Founded and built a machine identity security platform that maps AWS IAM, GitHub Actions OIDC, and Kubernetes relationships to expose overprivileged workloads, risky trust paths, and clear remediation ownership.
- Delivered a CLI, Docker image, API, and hosted web application at identrail.com, turning the security model into a deployable workflow.
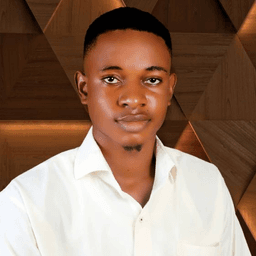
Oluwatobi Mustapha
About Me
I'm a security engineer who builds and secures cloud and distributed systems, with a focus on making complex environments more observable, resilient, and easier to operate.
My work spans cloud security, identity and access, detection engineering, incident response, vulnerability management, and security automation. Across AWS, Kubernetes, and open-source projects, I investigate attack paths, improve defensive workflows, and turn security findings into practical fixes.
When I'm not working, you'll find me playing chess, solving math problems, or playing FIFA.
Experience
- Build AI-assisted detection and triage workflows across application, cloud, IAM, CI/CD, and endpoint signals, improving alert quality and investigation context for analysts.
- Translate security findings into validated remediation guidance and operator-ready workflows, connecting detection design to response and root-cause analysis.
- Delivered cloud and identity security engineering across AWS, Keycloak, Terraform, Authentik, Better Auth, and Cloud Custodian.
- Contributed upstream security fixes for authentication, OTP-bypass, and IAM-monitoring issues, and built JIT-access and privilege-analysis tooling.
- Performed vulnerability assessments and penetration tests on Linux-based targets using Burp Suite, Nmap, and Metasploit, reproducing findings across web and system attack surfaces.
- Identified OWASP Top 10 risks, including injection, broken authentication, and access-control weaknesses, then produced severity-ranked remediation reports.
- Supported incident-response investigations and root-cause analysis while hardening Linux systems through firewall and access-control reviews.
- Helped establish security operations processes as an early security-team member, replacing ad-hoc response with repeatable workflows.
- Co-authored incident-response playbooks and runbooks covering triage, escalation, containment, recovery, and post-incident review.
- Standardized vulnerability-management and security-investigation workflows, partnering with engineering to turn findings into actionable remediation.
Projects
Identrail
Open-source machine identity security platformGives security teams one explainable view of how repositories, workloads, and cloud roles connect, so overprivileged machine identities and risky trust paths are found before they become incidents.
Preview
Fintech SOC Assessment
45-page fintech SOC assessmentConducted an independent 45-page fintech security operations assessment spanning SIEM alert triage, detection engineering, AWS incident response, vulnerability validation and remediation, compliance and posture reporting, and executive security metrics. Used Datadog Cloud SIEM to investigate a 47-signal queue, make evidence-led containment judgments, evaluate KRI/KPI integrity, MTTR and log coverage against SLA, and define responsible AI guardrails without overstating what the data could prove.
Boundary
Serverless AWS access brokerReplaces standing privilege with approval-based, short-lived access that is automatically revoked and easy to audit.
IAM Logic Fuzzer
AWS IAM analysis toolCatches dangerous IAM policy combinations before deployment, including confused-deputy paths, privilege escalation, public exposure, and permission-boundary flaws.
Architecture diagram
Modernizing EKS Workload Identity
IRSA-to-Pod Identity migrationConducted a hands-on migration from OIDC-based IRSA to Amazon EKS Pod Identity, preserving least-privilege IAM access while validating STS credential delivery and private S3 access.
Architecture diagram
EDR Simulation
Endpoint detection and response labValidated endpoint prevention and investigation in a controlled Windows lab by triggering the EICAR test, reviewing quarantine telemetry, and mapping the event to MITRE ATT&CK.
Network Traffic Analysis
Malware traffic investigationAnalyzed a malware-infected PCAP to trace NetSupportRAT command-and-control traffic, extract indicators, identify the compromised user, and connect the activity to its initial access path.
Incident Response Investigation
Endpoint and network forensicsReconstructed a suspected Qakbot intrusion by correlating PCAP evidence, VirusTotal intelligence, PowerShell file hashes, and Splunk telemetry to confirm exfiltration and trace the attack path.
AWS Honeypot
Cloud threat detection labDeployed an internet-facing AWS honeypot and used Kibana telemetry to observe brute-force activity, attacker origins, and real-world probing against exposed SSH and FTP services.
Open Source Contributions
Hardened enterprise identity flows across authorization, federation, OIDC, token exchange, session cleanup, and audit pagination, reducing privilege-escalation risk and improving policy and audit reliability. Most recently, restricted Twitter request-token deserialization to expected classes, reducing unsafe-input risk without disrupting valid callbacks.
ViewClosed four authentication edge cases: blocked race-condition reuse of one-time codes, enabled session activation using signed multi-session cookies, preserved cookie values during refresh, and aligned session responses with OpenAPI 3.1, improving account security and client interoperability.
ViewAcross six fixes, improved OAuth recovery and integration reliability: distinguished reauthentication from transient Google token failures, normalized Hive usernames, surfaced failed Abode actions, removed legacy Supervisor refresh tokens, and redacted sensitive Z-Wave add-on errors.
ViewFixed AWS provider credential precedence so an explicitly configured web-identity token is not rejected when an environment token file is present, while preserving validation for conflicting sources and existing environment-only configurations.
ViewImproved identity and administration flows across four fixes: reset stale MFA challenge selections, disambiguated duplicate RBAC permissions, decoded form-encoded OAuth client credentials correctly, and handled list-valued FreeIPA password-change timestamps during LDAP sync.
ViewStrengthened three cloud-governance paths: matched IAM condition keys using AWS case-insensitive semantics, preserved genuine AccessDenied errors during user lookup, and sanitized Lambda VPC data so Security Hub findings pass schema validation.
ViewFixed v1 gateway error translation to preserve native gRPC authentication statuses, so unauthenticated API requests return HTTP 401 instead of 500; aligned activity reporting and added regression coverage across the converter, middleware, and gateway.
ViewSecurity-reviewed LEAP Stacks, an AWS launchpad for AI agents, with attention to IAM boundaries, infrastructure deployment, observability, and cost controls, providing practical safeguards when evaluating prototypes under real cloud conditions.
ViewTestimonials

Bereket Engida
CEO of Better Auth
Thank you @Oluwatobi-Mustapha for the PR fix and update, LGTM.

Alexander Schwartz
Principal Software Engineer at IBM
As I've raised the original issue, I've tested this change it and it works as expected. Thanks, Oluwatobi!

AJ Kerrigan
Solutions Architect at Stacklet
Thanks for the catch/fix/test Oluwatobi Mustapha ๐ป !

Martin Hjelmare
Home Assistant Core Developer
Looks good to me, Tobi! Thanks!

Basil Fateen
Head of Startups and VC, MENAT at NVIDIA
Thanks for your security review and updates, Oluwatobi!

Victor Wilkis-Ehizojie
AI Fraud Detection Consultant @ Probuilt Tech
I worked with Oluwatobi at Probuilt Tech and always found him easy to work with. He helped us improve how we handled security issues, from incident response to vulnerability management, and worked well with the engineering team whenever fixes were needed. He was proactive, practical, and someone I could rely on.

Teffen Ellis
Senior Full-stack Developer at Authentik Security and sister-software
Thank you sending such a detailed PR, Oluwatobi Mustapha! The changes here look great and align with an ongoing effort to make the flow stages easier to test and reason about.

Marek Posolda
Principal Software Engineer at IBM
Thanks for the updates and PR review.

Gayathri Vijayan
Software Engineer at ZITADEL
Thank you very much for the contribution, Oluwatobi. Great job! Please keep contributing to Zitadel :)

Kapil Thangavelu
Co-Founder & CTO at Stacklet
This looks good to me. Thank you.

Stefan Agner
Senior Security Engineer @ Home Assistant
Great work on this. The Unix socket approach has now proven reliable across multiple releases, making the old Supervisor token obsolete. This was a clean and well-timed removal of unnecessary legacy authentication. LGTM ๐

Pedro Igor
Principal Software Engineer @IBM
Thank you, @Oluwatobi-Mustapha for your PR fix and updates. Merged!

Kit Ewbank
Principal Software Engineer @ HashiCorp
LGTM ๐. @Oluwatobi-Mustapha Thanks for the contribution๐ ๐.

Stan Silvert
Principal Core Developer at Red Hat
LGTM. Copilot and Claude also agree it's ready to merge.
Technical Toolkit
Cloud & Platform Security
Identity & Access
Security Operations
Community
Let's Connect
Open to opportunities in Cloud Security, Identity Security, Detection Engineering, and Security Operations Engineering.